
Astra Security launches free tools to help organisations identify PHP2Shell vulnerabilities

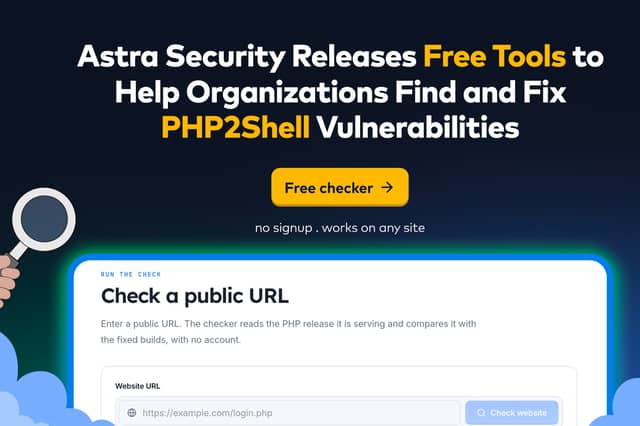

Astra Security has released two free tools to help organisations assess their exposure to the recently disclosed PHP2Shell vulnerabilities and support remediation efforts.
Astra Security has released two free resources to help organisations respond to PHP2Shell, the critical PHP vulnerabilities disclosed this week.
The first is a public-facing PHP2Shell Checker, while the second, php2shell-triage, is an open-source tool designed to support deeper investigations and remediation efforts.
The vulnerabilities, CVE-2026-109618 and CVE-2026-109619, are both rated 9.2 on CVSS v4.0 and can allow unauthenticated remote code execution through PHP's core runtime.
Fixes are available in PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35. With PHP widely used across websites, CMS platforms, custom applications and vendor-managed infrastructure, organisations may need to assess systems beyond the applications they directly maintain.
The PHP2Shell Checker compares the PHP version a public website appears to be running against the fixed releases. It requires no account and is intended to provide an initial indication of potential exposure. However, Astra notes that proxies, hosting providers and server configurations can hide or alter version information, while a clean result does not provide visibility into internal systems.
For organisations assessing their own infrastructure, php2shell-triage helps teams examine PHP runtimes across server APIs, identify stale workers, look for indicators of exploitation and plan remediation. The read-only script inspects the binaries behind running PHP workers rather than relying on command-line version information, helping to identify situations where servers appear patched but are still running vulnerable workers.
Astra recommends organisations identify affected installations, apply available updates, restart PHP workers and confirm patched runtimes are active. Where compromise is suspected, evidence should be collected before systems are restarted. Organisations running end-of-life PHP versions, including 8.1 and earlier, will need to plan upgrades as those releases will not receive official fixes. Where patching is not immediately possible, Astra suggests isolating vulnerable systems.
Shikhil Sharma, founder and CEO at Astra Security, said: "During a disclosure like PHP2Shell, the hardest question isn't 'Are we vulnerable?' It's 'What is actually running right now?'"